
Govern every Keycloak OAuth client from one dashboard.
Taco connects to Keycloak to inventory OAuth and OpenID Connect clients, validate new client requests, control scopes and audiences, and keep an audit trail of every change.
Your Keycloak tenant has more OAuth clients than anyone can explain.
Every team registers its own apps. Redirect URIs drift, secrets are never rotated, and nobody remembers who owns the client with full API access. Taco brings order to Keycloak client management without changing how tokens are issued.
Who owns this Keycloak client?
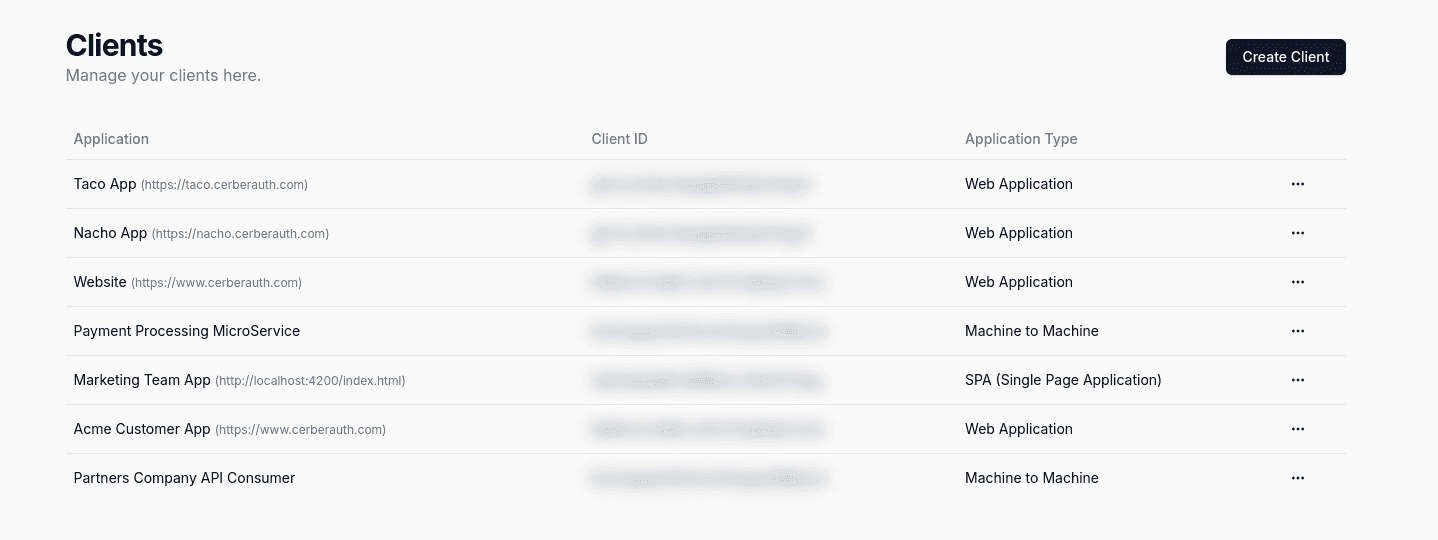
Taco builds an inventory of every OAuth and OpenID Connect client in Keycloak, with owners, environments, and custom metadata your team can actually search.
Anyone with console access can create a client.
Route new Keycloak client requests through validation and approval. Grant types, redirect URIs, and scopes are checked against your policies before the client exists.
This client should not have access to that API.
Review and restrict scopes and audiences per client, and see at a glance which applications can call your most sensitive APIs.
Keycloak OAuth clients
A governance layer for your Keycloak clients.
Taco connects to the Keycloak admin APIs and manages OAuth and OpenID Connect clients on your behalf: creation, updates, approvals, and reviews.
Keycloak keeps issuing tokens and running your authorization flows. Taco makes sure the clients it serves are the ones you actually approved.
Nothing to migrate
Existing Keycloak clients are imported as-is. Your apps keep their client IDs and flows.
Policy before creation
Grant types, redirect URIs, and scopes are validated before a client reaches Keycloak.
Full traceability
Every client change, approval, and secret rotation is recorded with who did it.
Connect your Keycloak environment
Give Taco admin API credentials for each Keycloak environment you want to govern.
Import and tag existing clients
Assign owners, environments, and metadata to the clients already registered in Keycloak.
Enforce your client policies
New clients and changes go through validation and approval before they are applied in Keycloak.
Best for IAM and platform teams running Keycloak across several teams or environments who need to know which clients exist and why.
Every Keycloak client. Known, owned, and approved.
Taco sits next to Keycloak, not in front of it. Token issuance stays untouched — Taco manages the client configuration that Keycloak relies on.
🗂️
One inventory for all your Keycloak clients.
See every OAuth and OpenID Connect client registered in Keycloak, across environments, with its owner, grant types, and last change. Add custom metadata so the inventory reflects how your organization works.
billing-web
authorization_code · owner: payments
reporting-batch
client_credentials · owner: data
test-app-2
implicit · owner: unknown
✅
Validate clients before they reach Keycloak.
Teams request clients through Taco. Grant types, redirect URIs, and requested scopes are checked against your policies, and sensitive requests go to the right approver before anything is created in Keycloak.
🛡️
A clear history for every client change.
Creations, scope changes, secret rotations, and approvals are logged with the requester and the approver. When a security review asks why a client can call an API, you have the answer.
Ready to get started?
Taco connects to Keycloak to inventory OAuth and OpenID Connect clients, validate new client requests, control scopes and audiences, and keep an audit trail of every change.
Request early access